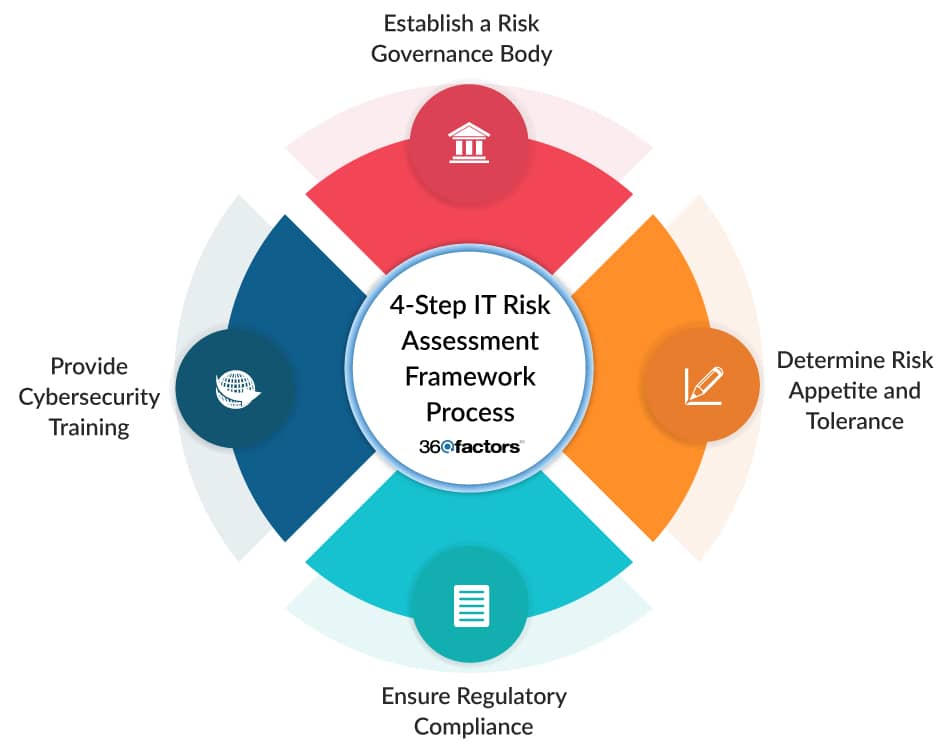
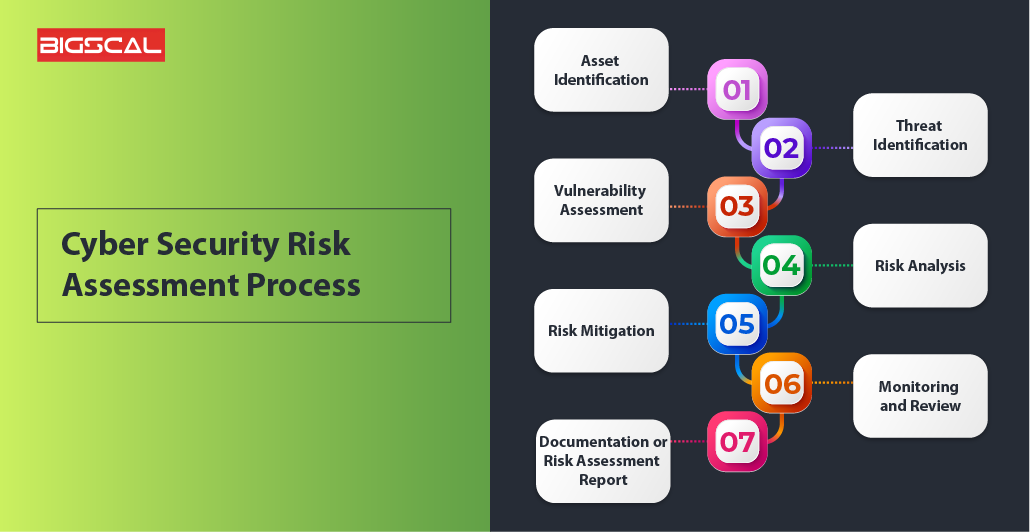
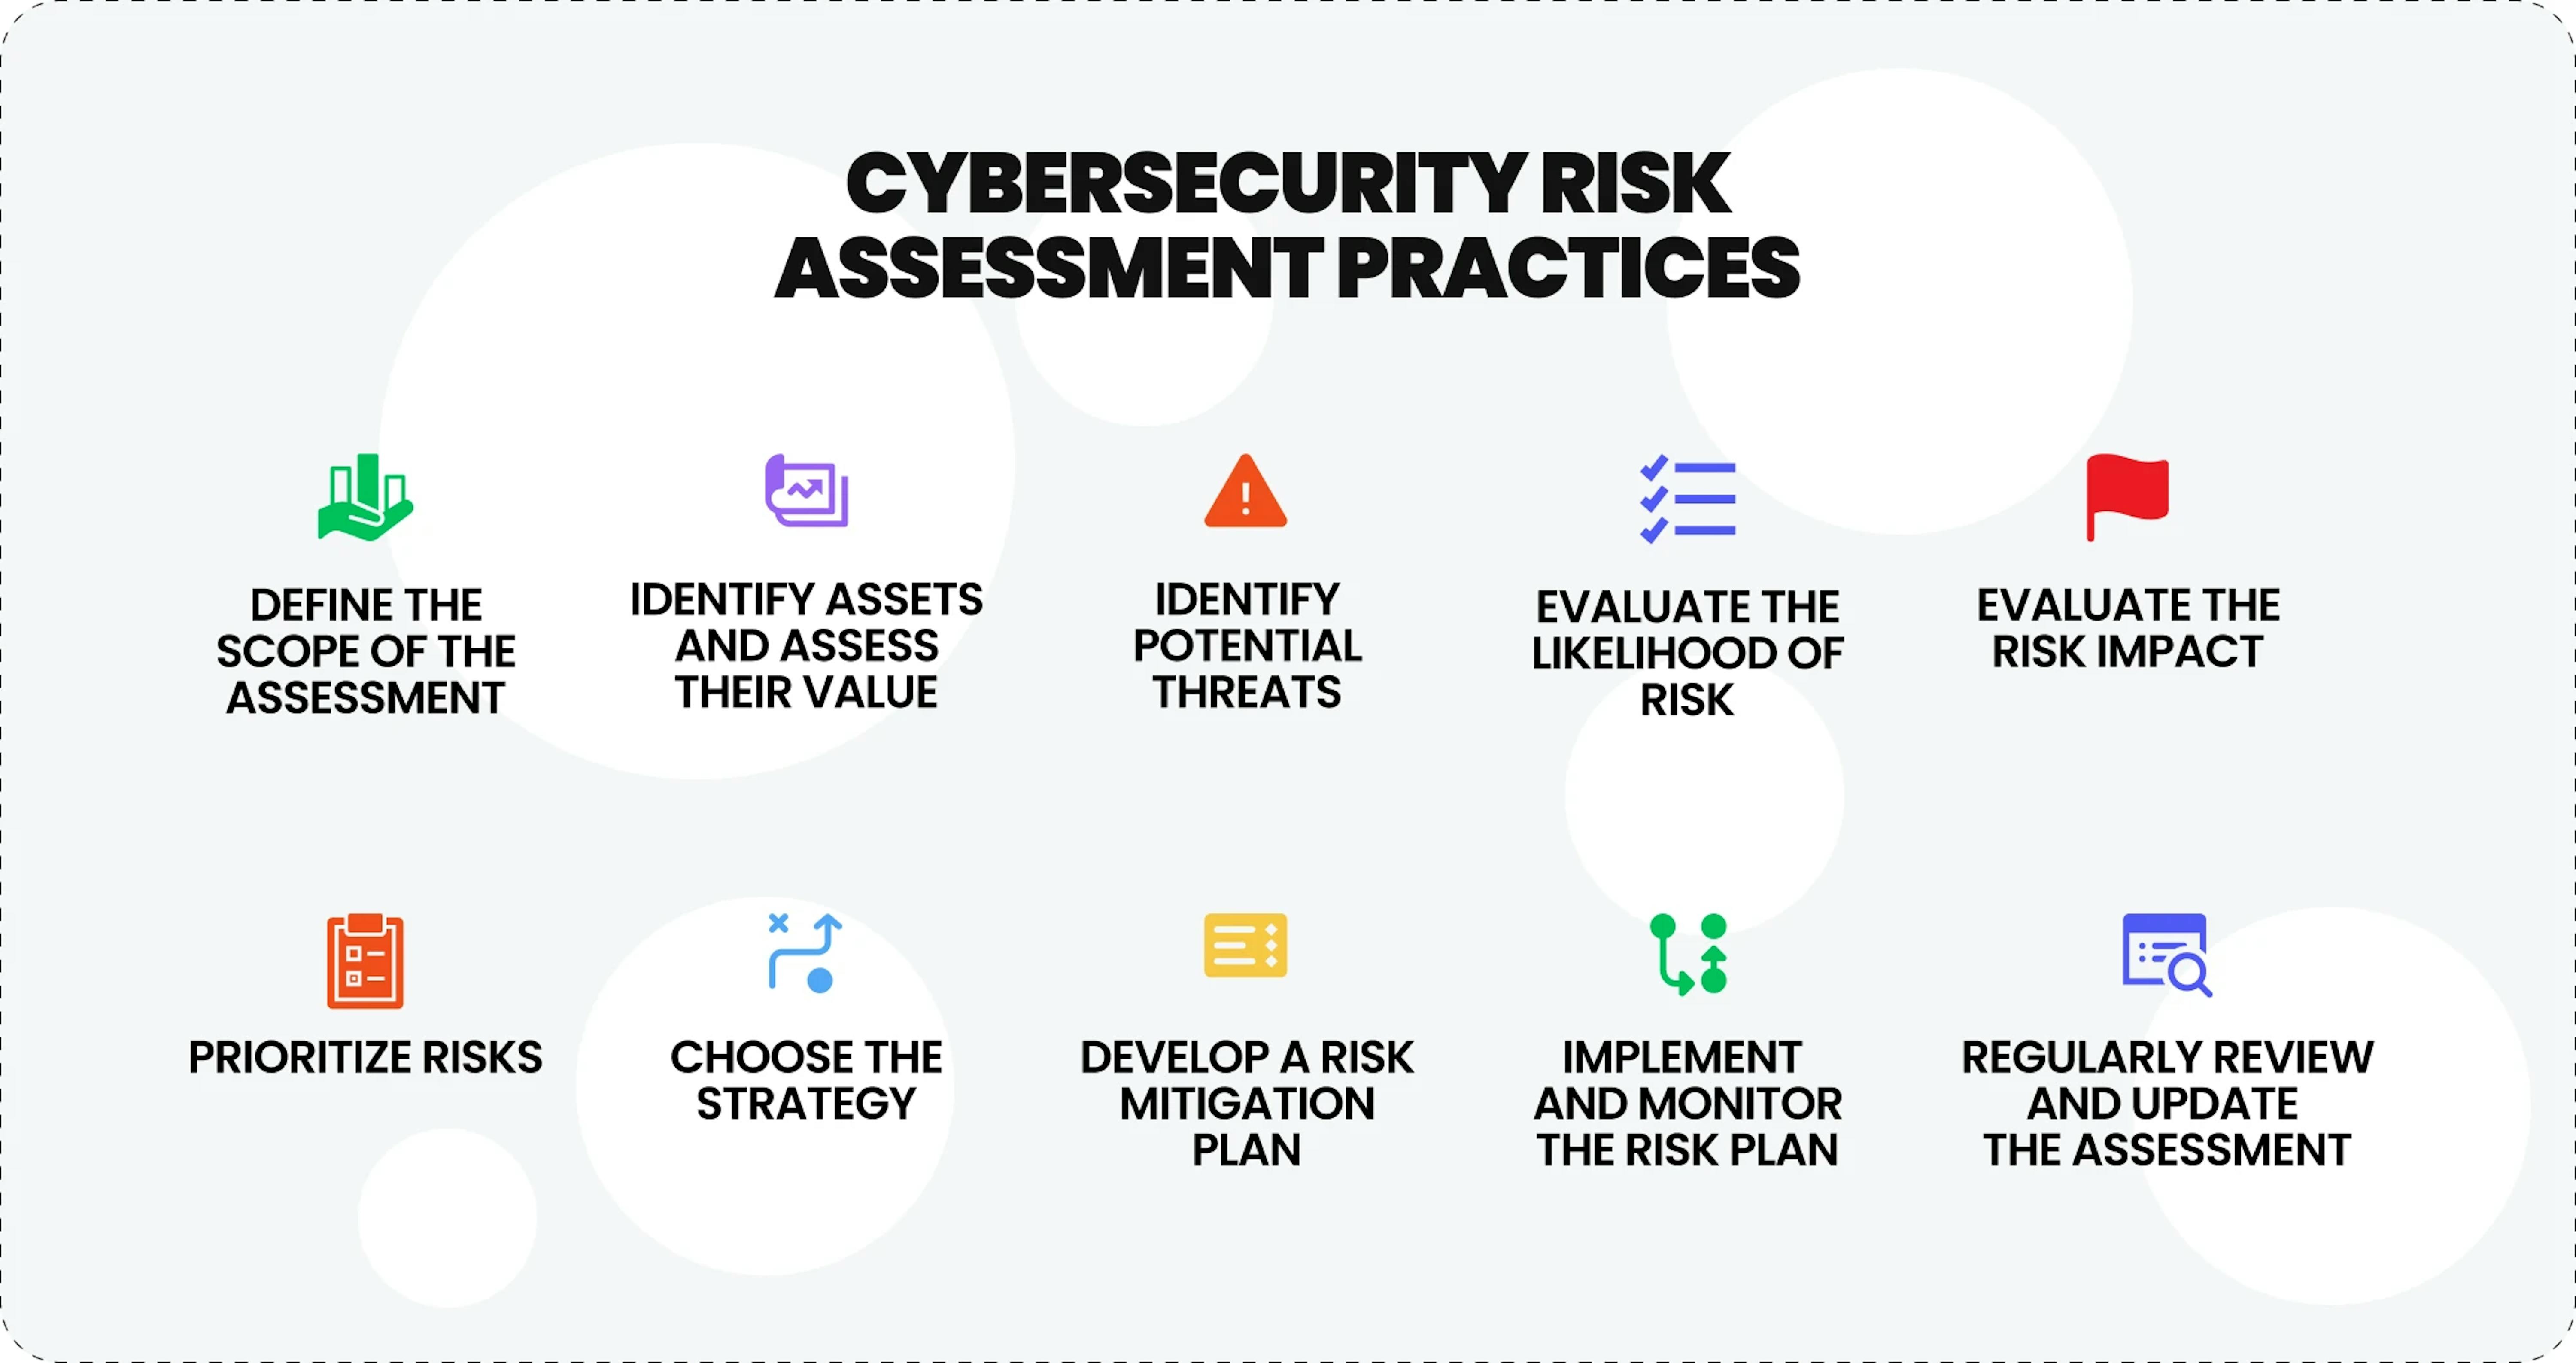
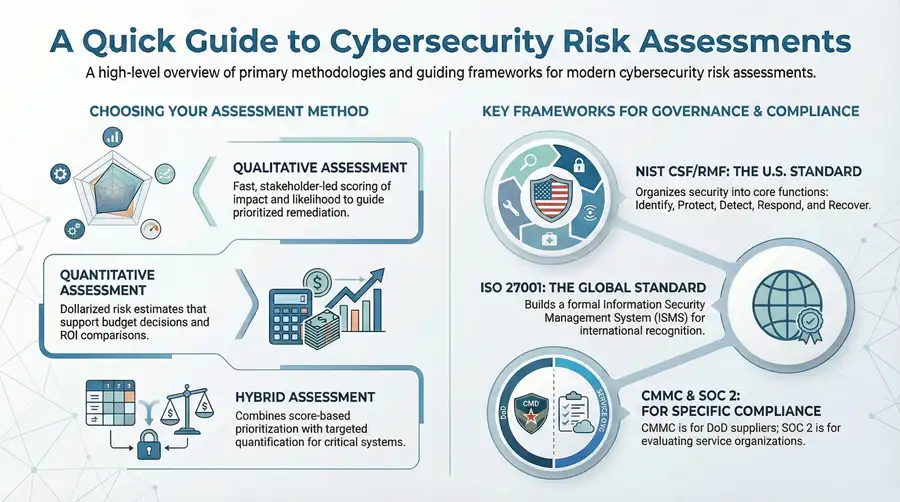
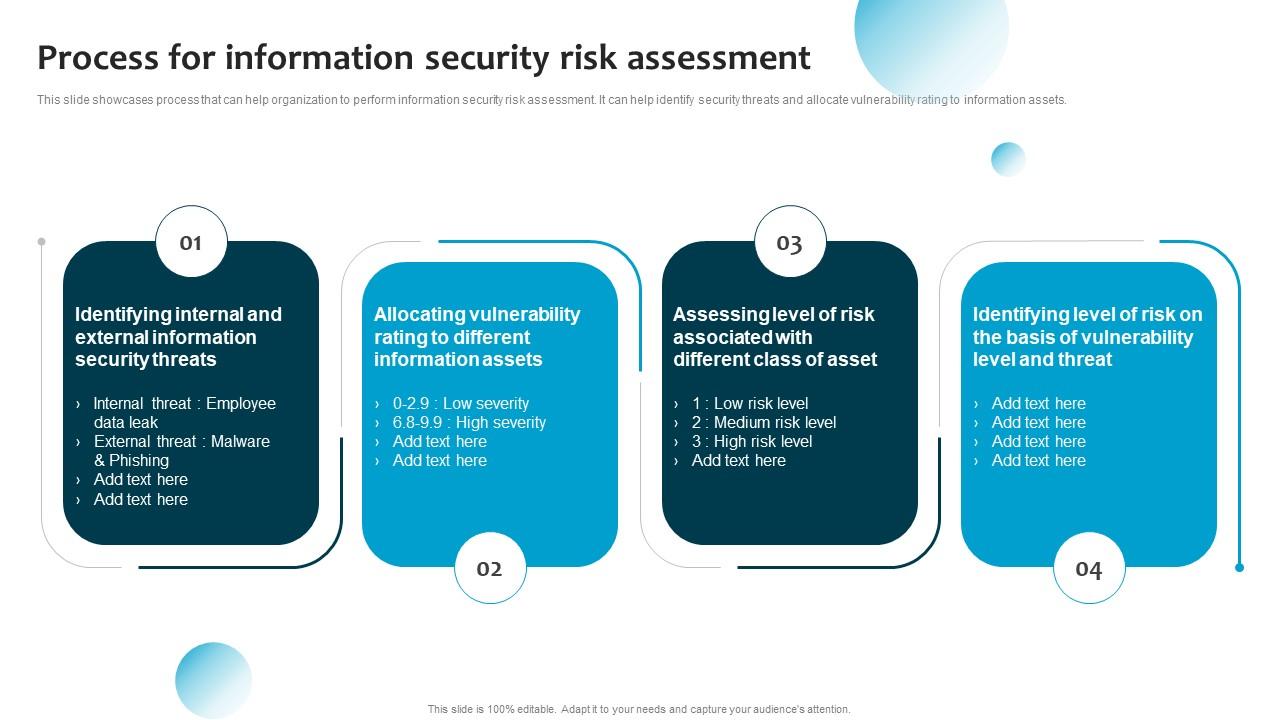
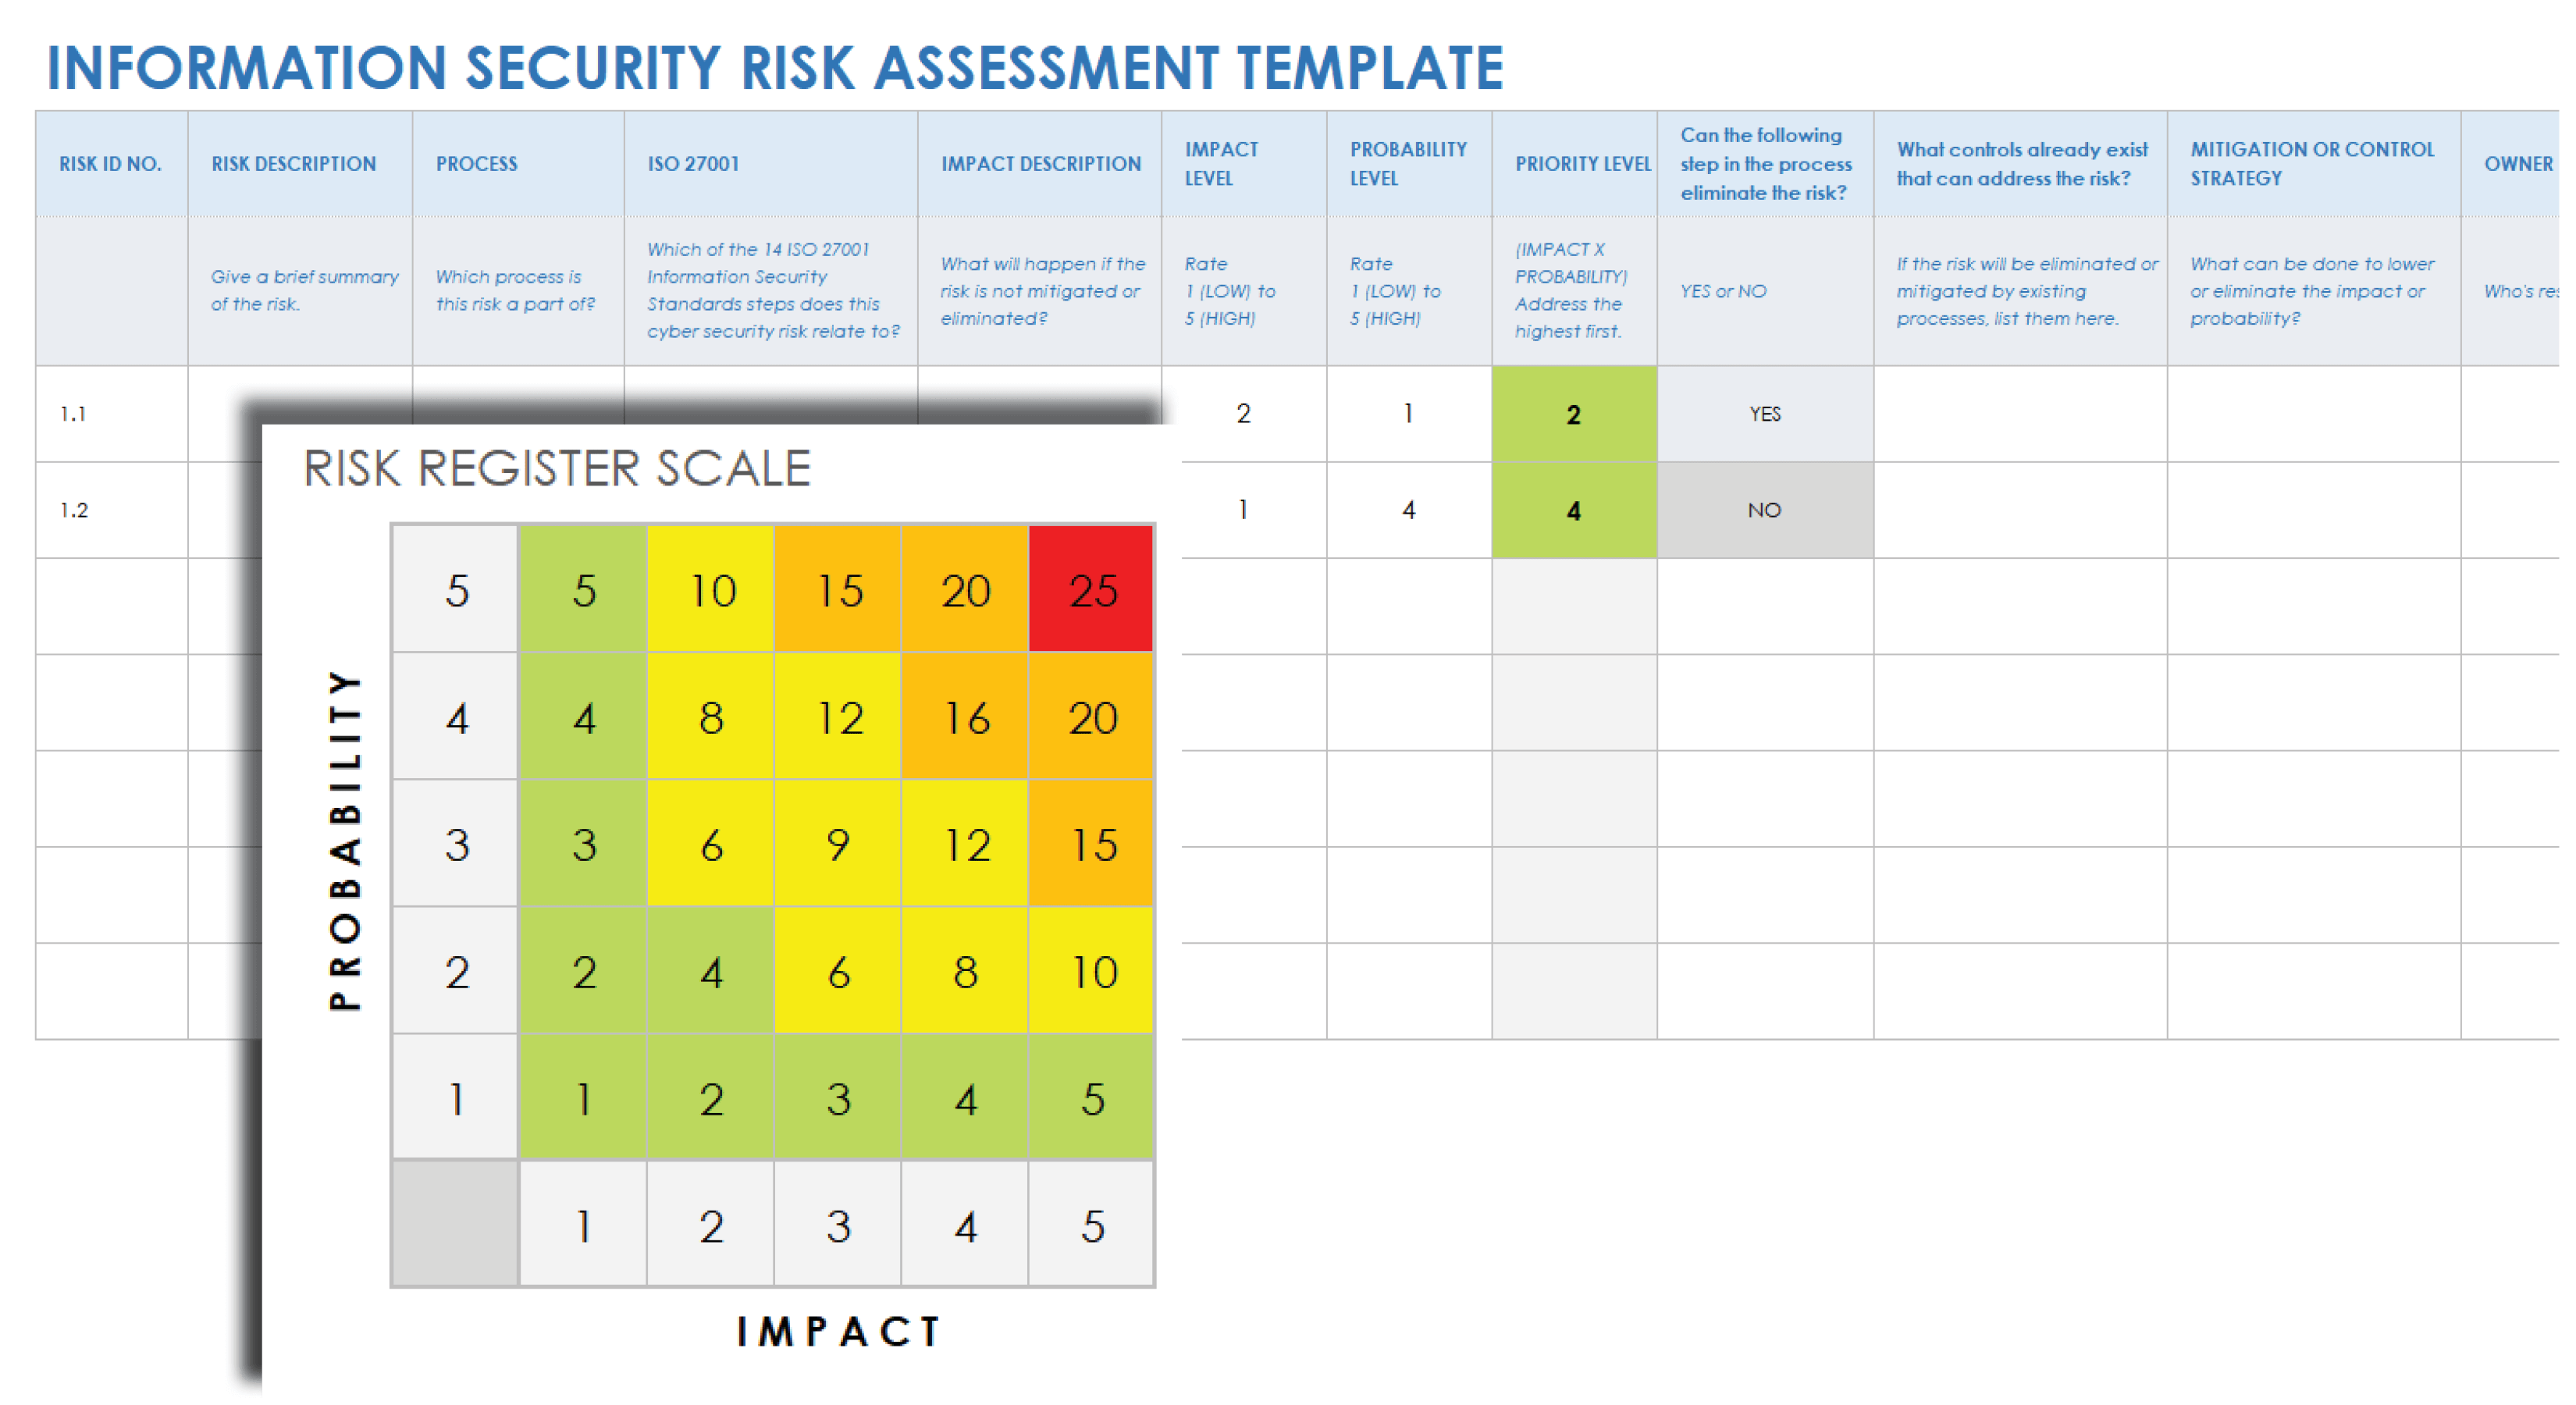
management is risk assessment: the means by which risks to systems are identified and evaluated to justify. security controls.The objective of this report is to examine the applicability of current risk assessment techniques to assess modern electronic threats.
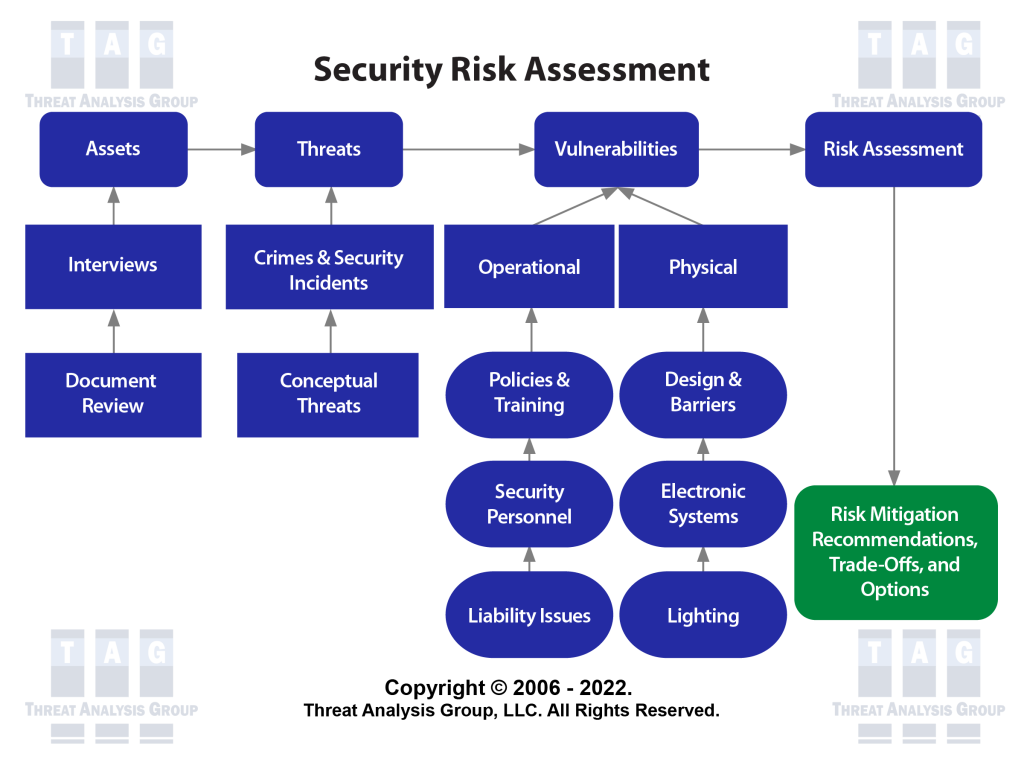
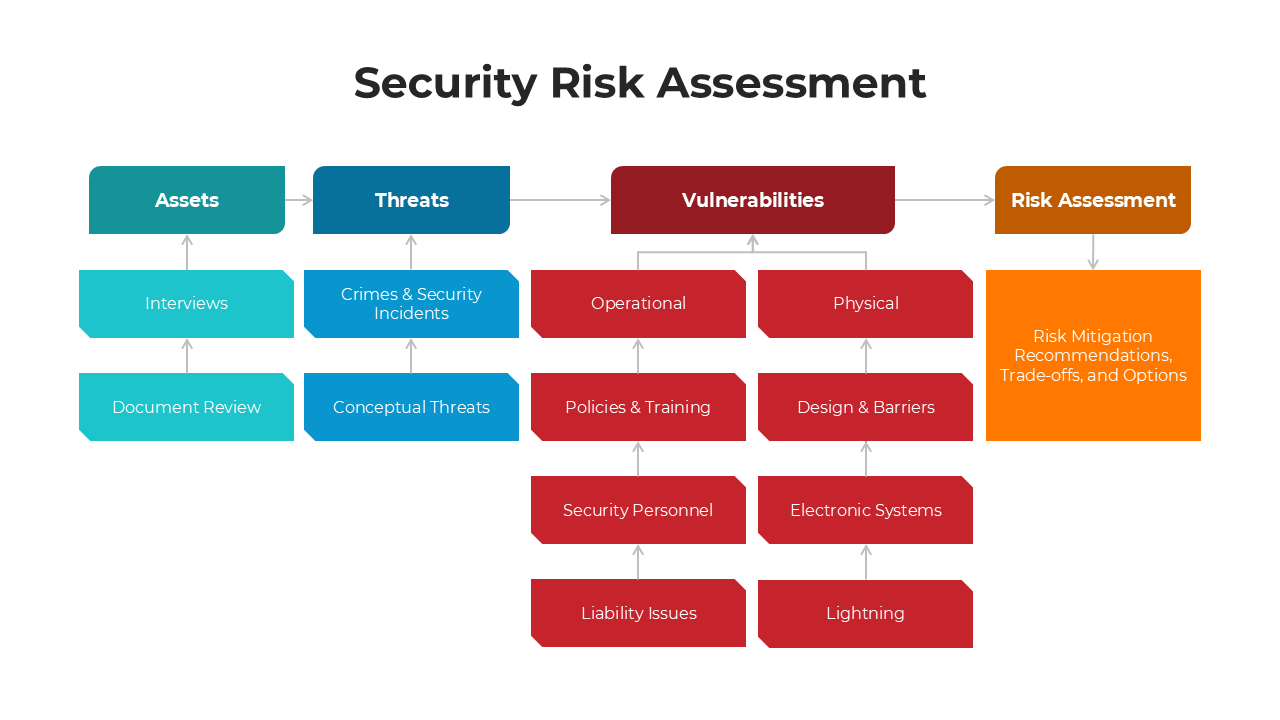
The document discusses IT security management and risk assessment, outlining key terminology such as assets, threats, vulnerabilities, and risks.
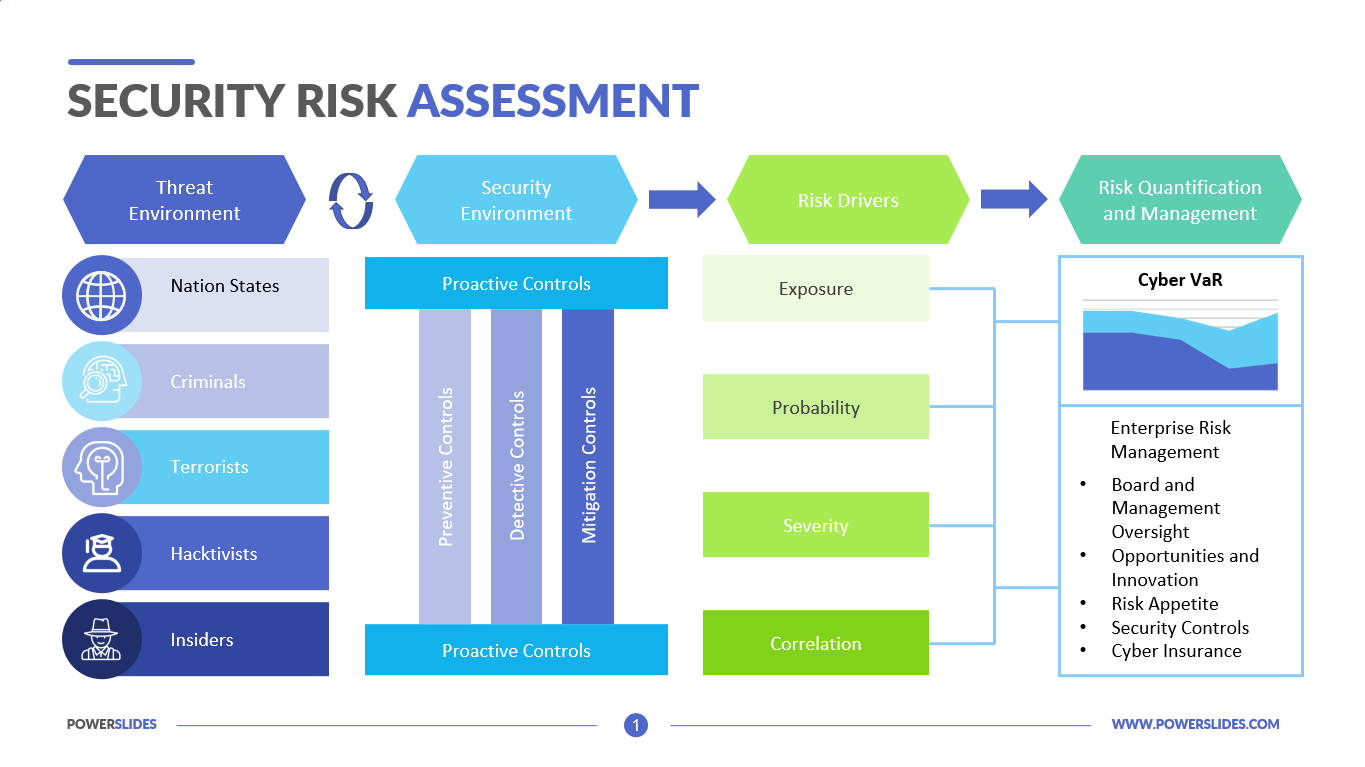
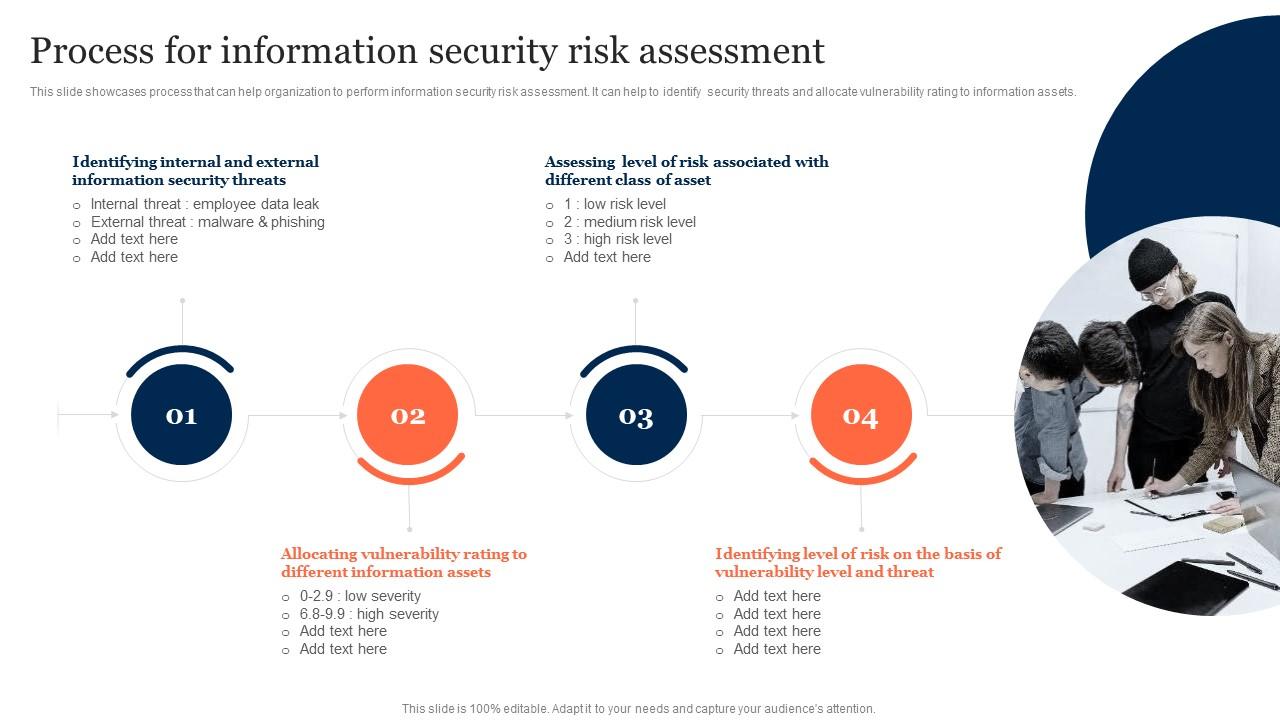
Security Risk Assessment is a specific subset of risk management. It particularly focuses on security threats and vulnerabilities found within an organizations infrastructure, systems, and processes. Purpose and Objectives.
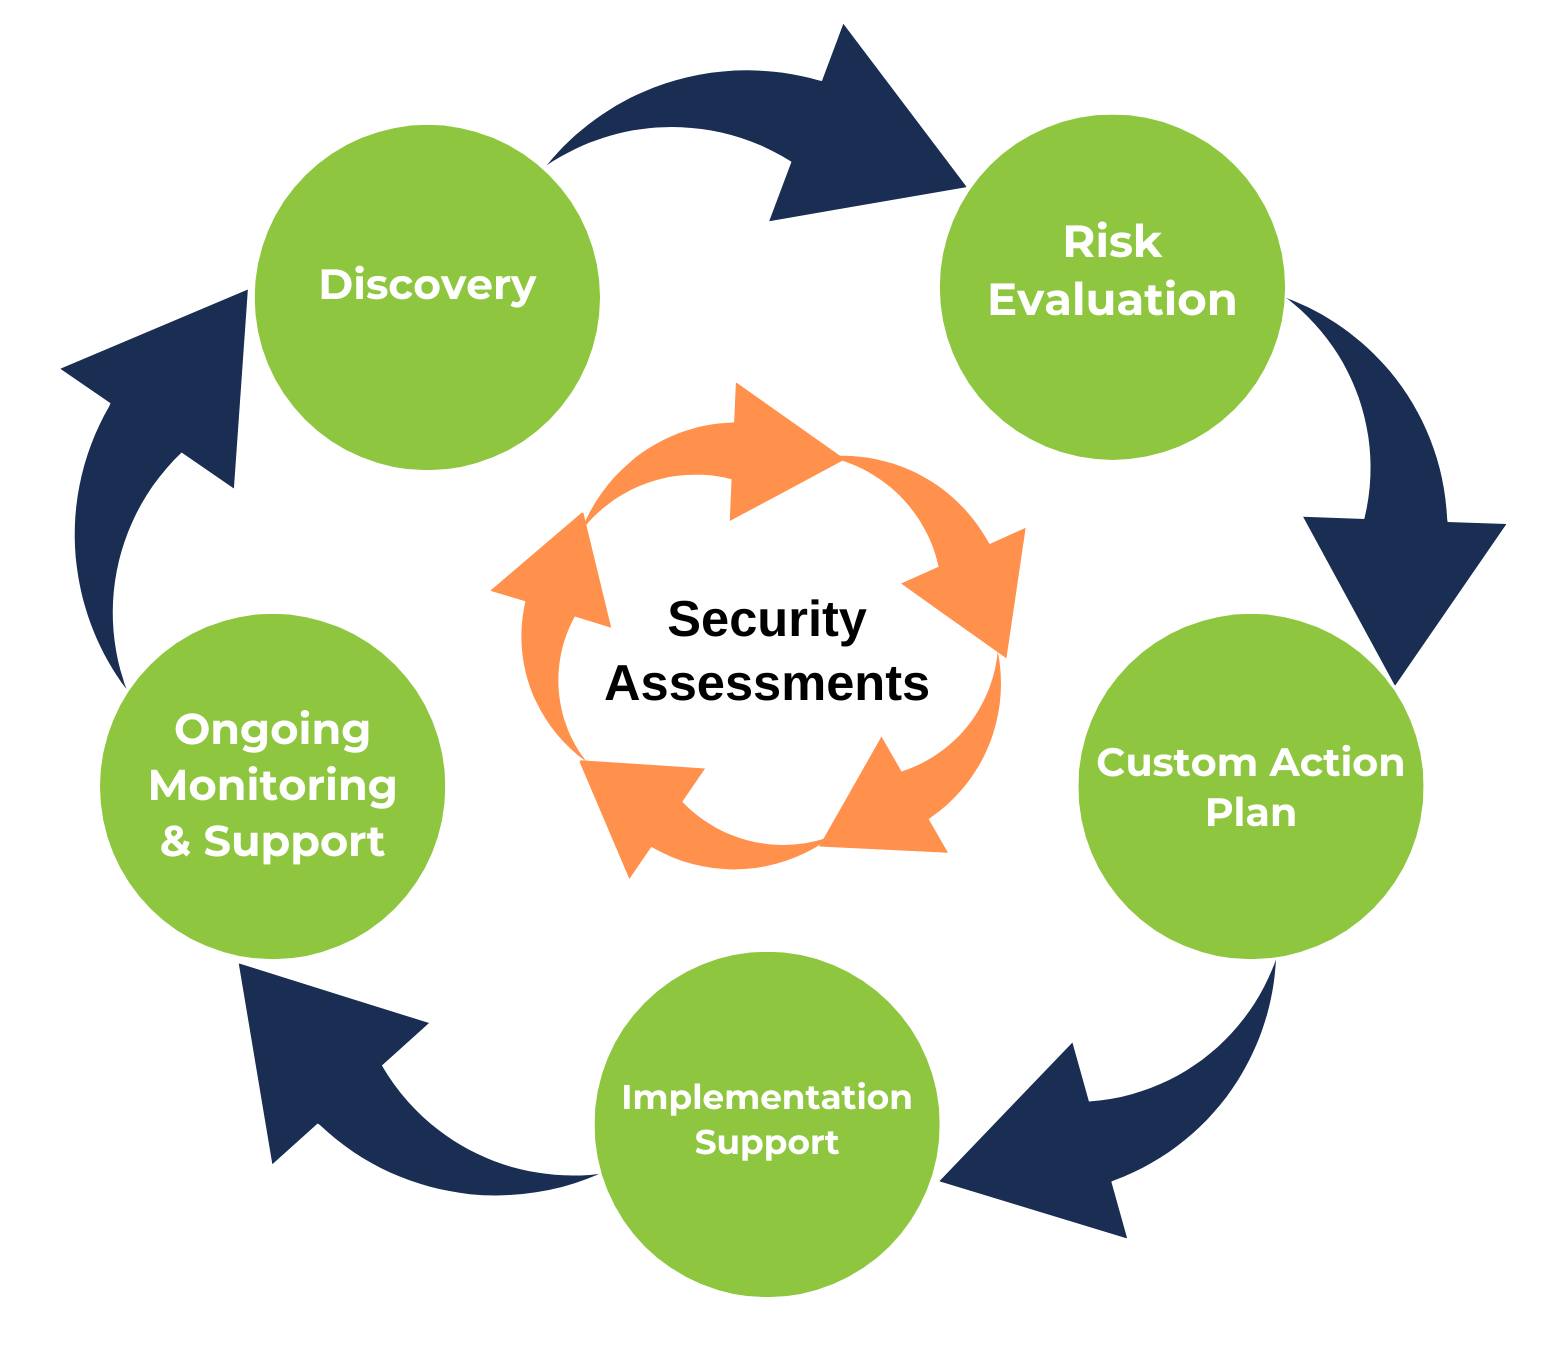
Moving forward, it's essential to keep these visual contexts in mind when discussing Electronic System Security Risk Assessment.
Learn the essentials of ISO 27001 risk assessment, managing risks, and steps to protect your organization's information security.
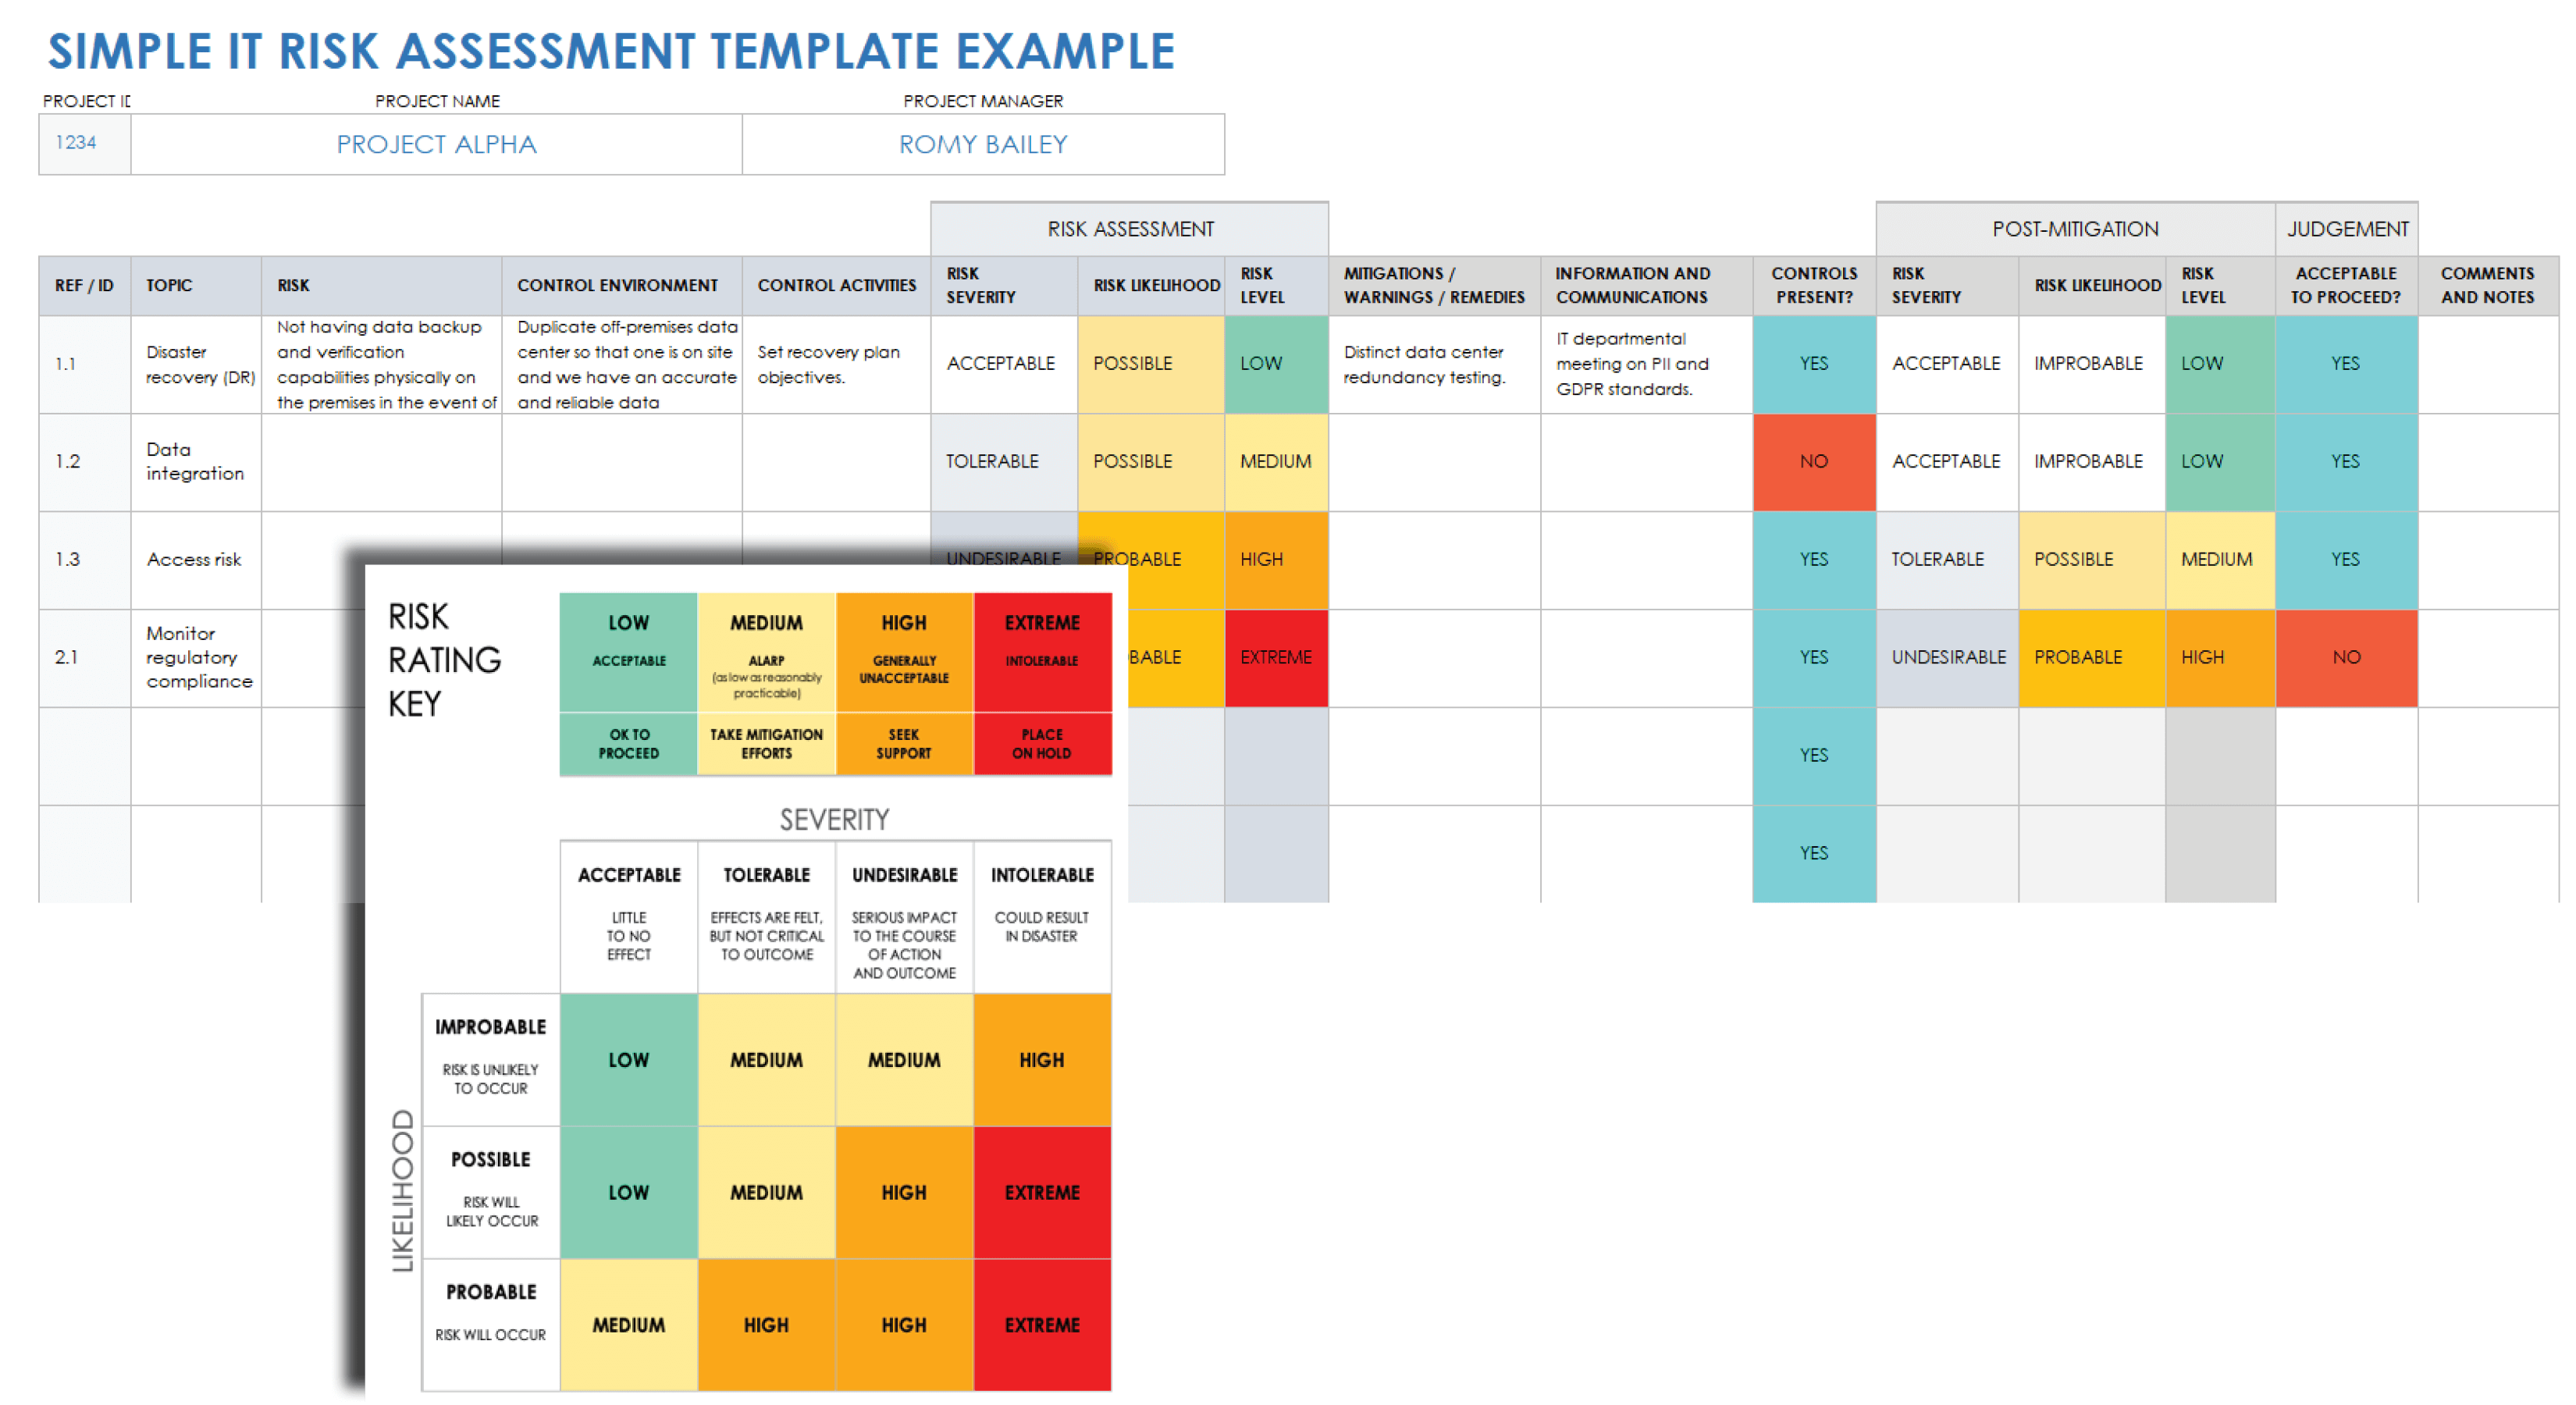
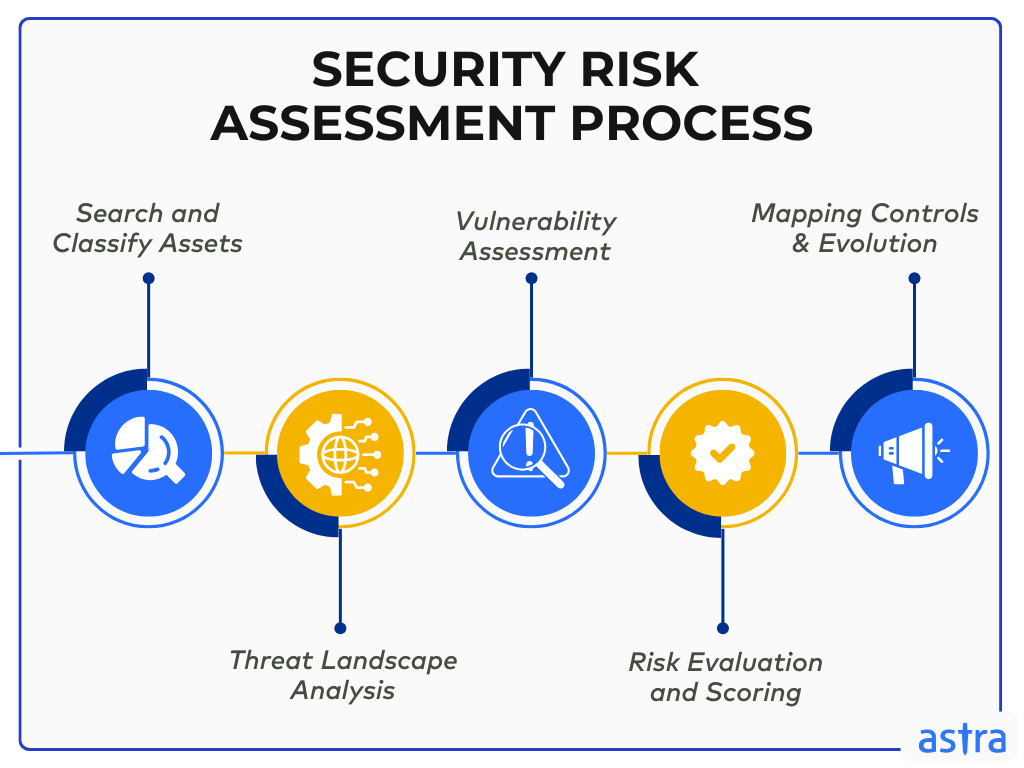
A cyber security risk assessment is a structured process used to evaluate an organisation's current technology, security controls, policies, and procedures to identify potential threats to its critical assets and data.

Turnkey Consulting's Information Security Risk Assessment methodology involves nine primary steps which help in conducting an information risk assessment.
This paper reviews the state of the art in cyber security risk assessment of Supervisory Control and Data Acquisition (SCADA) systems. We select and in-detail examine twenty-four risk assessment methods developed for or applied in the context of a SCADA system.